
Multicloud AI & ERP / Cloud Networking, Edge & Zero Trust for AI
Why it matters
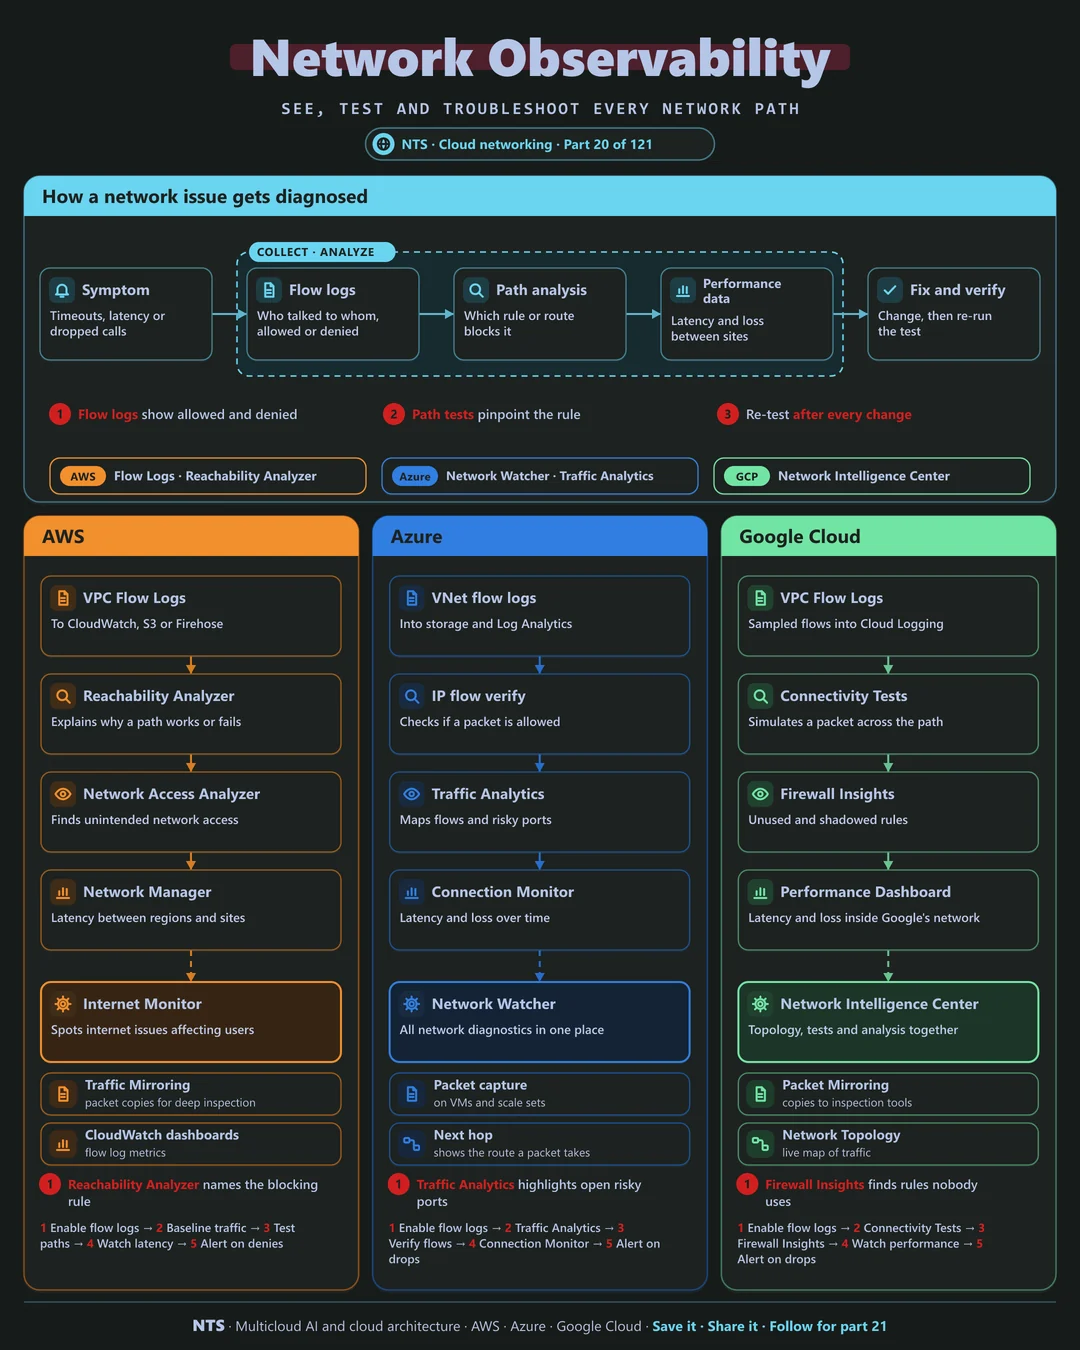
Network issues are hard to see: they look like application timeouts, intermittent errors or slow pages. Without records and tools, teams guess, escalate and wait. With them, the blocking rule or broken route is found in minutes.
How it works
Record, analyze, test
Flow logs record who talked to whom, on which port, and whether it was allowed. Path analysis tools simulate a packet through routes and firewall rules and name the exact rule that blocks it. Performance monitoring tracks latency and loss between regions and sites over time.
Prevent, not just diagnose
The same tools find risky configurations before incidents: unused or overly broad firewall rules, unintended internet exposure and paths that should not exist.
AWS, Azure and Google Cloud compared
| AWS | Azure | Google Cloud | |
|---|---|---|---|
| Flow records | VPC Flow Logs | VNet flow logs | VPC Flow Logs |
| Path analysis | Reachability Analyzer | IP flow verify, next hop | Connectivity Tests |
| Exposure analysis | Network Access Analyzer | Traffic Analytics | Firewall Insights |
| Performance | Network Manager, Internet Monitor | Connection Monitor | Performance Dashboard |
| Packet capture | Traffic Mirroring | Packet capture | Packet Mirroring |
| All-in-one hub | Network Manager | Network Watcher | Network Intelligence Center |
What makes each cloud different
AWS
AWS Reachability Analyzer explains exactly why a path works or fails, naming the security group, route or ACL involved. Network Access Analyzer finds unintended access, and Internet Monitor spots internet problems affecting your users.
Azure
Azure Network Watcher bundles diagnostics: IP flow verify, next hop, packet capture and Connection Monitor for latency and loss over time. Traffic Analytics maps flows and highlights risky open ports.
Google Cloud
Google's Network Intelligence Center offers Connectivity Tests that simulate packets across the path, Firewall Insights that find unused and shadowed rules, and a live topology map of traffic between workloads.
Design decisions that matter
- 01Flow logs on before go-live
Keep at least 30 days searchable.
- 02Path tests after every network change
Make them part of the change process.
- 03Alert on denies for critical paths
Unexpected blocks are early warnings.
- 04Review exposure monthly
Find unused and risky rules.
Common mistakes we see
- Logging only after an incident. The evidence you need is already gone.
- Guessing at firewall rules. Hours lost that path analysis saves.
- Ignoring rule hygiene. Shadowed and unused rules hide real risks.
A practical 30-day plan
- Week 1
Enable flow logs across all production networks.
- Week 2
Build dashboards and alerts for denied traffic.
- Week 3
Add path tests to the network change process.
- Week 4
Run an exposure and rule-hygiene review.
How NTS helps
NTS sets up network observability across AWS, Azure and Google Cloud: flow logging, dashboards, path testing in change processes and regular exposure reviews, cutting network troubleshooting from hours to minutes.
What you get
- Flow logs enabled and analyzed across clouds
- Connectivity and reachability tests
- Network dashboards and alerts
- Troubleshooting runbooks for common issues
Typical outcomes
- Faster resolution of network incidents
- Early detection of unusual traffic
- Evidence for security and compliance reviews
How we work with you
- 1Assess
A focused review of your network observability across AWS, Azure and Google Cloud. We look for the gaps we find most often: logging only after an incident, guessing at firewall rules and ignoring rule hygiene.
- 2Design
A target architecture and roadmap built on the decisions that matter most: flow logs on before go-live, path tests after every network change, alert on denies for critical paths and review exposure monthly.
- 3Build
Hands-on delivery alongside your team. We enable flow logs across all production networks, build dashboards and alerts for denied traffic, add path tests to the network change process, and finally run an exposure and rule-hygiene review.
- 4Run and improve
We tune flow logging costs, refine alerts and extend coverage to new networks and regions.
Why teams choose NTS for network observability
- See every packet path
We give your teams clear visibility into how traffic really flows.
- Faster troubleshooting
Our runbooks turn hours of guessing into minutes of diagnosis.
- Security insight
Flow data reveals unexpected connections and exfiltration attempts.
Book a free 30-minute review
Talk to an NTS architect about your network observability on AWS, Azure and Google Cloud.