
Multicloud AI & ERP / Cloud & AI Security, Governance & Compliance
Why it matters
Without a landing zone, every team invents its own accounts, networks and security, and the platform team spends years retrofitting controls. With one, new teams start compliant in hours.
How it works
What a landing zone contains
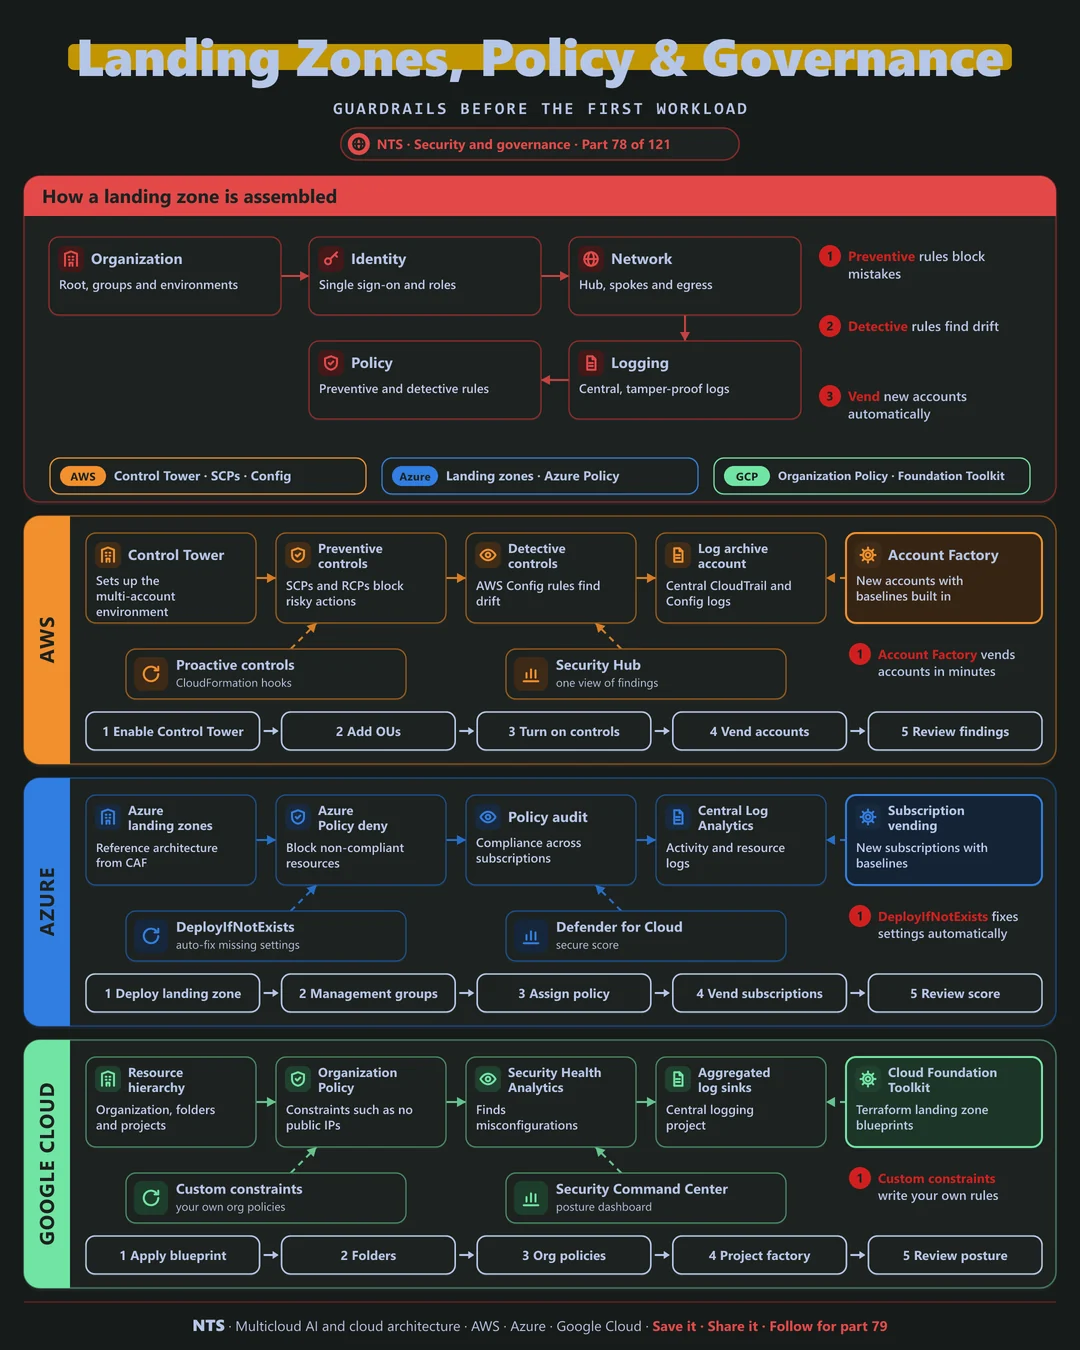
An organization structure with environments, identity with single sign-on, a network hub with controlled egress, central logging that teams cannot switch off, and policies: preventive rules that block mistakes and detective rules that find drift. Automated account vending gives every new team the same baseline.
AWS, Azure and Google Cloud compared
| AWS | Azure | Google Cloud | |
|---|---|---|---|
| Accelerator | AWS Control Tower | Azure landing zones | Cloud Foundation Toolkit |
| Preventive policy | SCPs, RCPs | Azure Policy deny | Organization Policy |
| Detective policy | AWS Config rules | Azure Policy audit | Security Health Analytics |
| Auto-remediation | Config remediation | DeployIfNotExists policies | Custom remediation with automation |
| Account vending | Account Factory | Subscription vending | Project factory |
What makes each cloud different
AWS
Control Tower sets up the multi-account environment with log archive and audit accounts, preventive and detective controls and Account Factory for new accounts in minutes.
Azure
Azure landing zones from the Cloud Adoption Framework provide a reference architecture with platform subscriptions, and DeployIfNotExists policies fix missing settings automatically.
Google Cloud
The Cloud Foundation Toolkit provides Terraform blueprints for the organization, folders, networks and logging, with custom organization policy constraints for your own rules.
Design decisions that matter
- 01Landing zone before workloads
Never retrofit.
- 02Everything as code
The landing zone is versioned like software.
- 03Preventive first, detective always
Block what you can, find the rest.
- 04Self-service vending
Teams get compliant accounts on demand.
Common mistakes we see
- Click-built foundations. Impossible to reproduce or audit.
- Too many exceptions. Guardrails become optional.
- Platform team as a bottleneck. Manual account requests take weeks.
A practical 30-day plan
- Week 1
Design the structure, policies and network.
- Week 2
Deploy the landing zone with the accelerator.
- Week 3
Add policies, logging and single sign-on.
- Week 4
Enable vending and onboard the first teams.
How NTS helps
NTS designs and deploys landing zones with Control Tower, Azure landing zones and the Cloud Foundation Toolkit, and modernizes existing ones, all as code with self-service vending.
What you get
- A landing zone on Control Tower, Azure landing zones or Google Cloud foundations
- Policies and guardrails as code
- Automated account and subscription vending
- Compliance dashboards
Typical outcomes
- Secure, compliant environments for every team
- New accounts ready in minutes
- Continuous compliance visibility
How we work with you
- 1Assess
A focused review of your landing zones and governance across AWS, Azure and Google Cloud. We look for the gaps we find most often: click-built foundations, too many exceptions and platform team as a bottleneck.
- 2Design
A target architecture and roadmap built on the decisions that matter most: landing zone before workloads, everything as code, preventive first, detective always and self-service vending.
- 3Build
Hands-on delivery alongside your team. We design the structure, policies and network, deploy the landing zone with the accelerator, add policies, logging and single sign-on, and finally enable vending and onboard the first teams.
- 4Run and improve
We evolve policies, add controls for new services and keep landing zones up to date.
Why teams choose NTS for landing zones and governance
- Governance that enables
Guardrails let teams move fast without breaking rules.
- Multicloud consistency
The same standards apply in every cloud.
- Automated from day one
Policies are enforced by code, not by meetings.
Book a free 30-minute review
Talk to an NTS architect about your landing zones and governance on AWS, Azure and Google Cloud.