
Multicloud AI & ERP / Cloud & AI Security, Governance & Compliance
Why it matters
Data protection laws such as GDPR, sector rules and customer contracts set where data may be processed. AI adds new data flows (prompts, caches, logs, vector indexes and fine-tuning sets) that are easy to overlook.
How it works
Keeping data in place
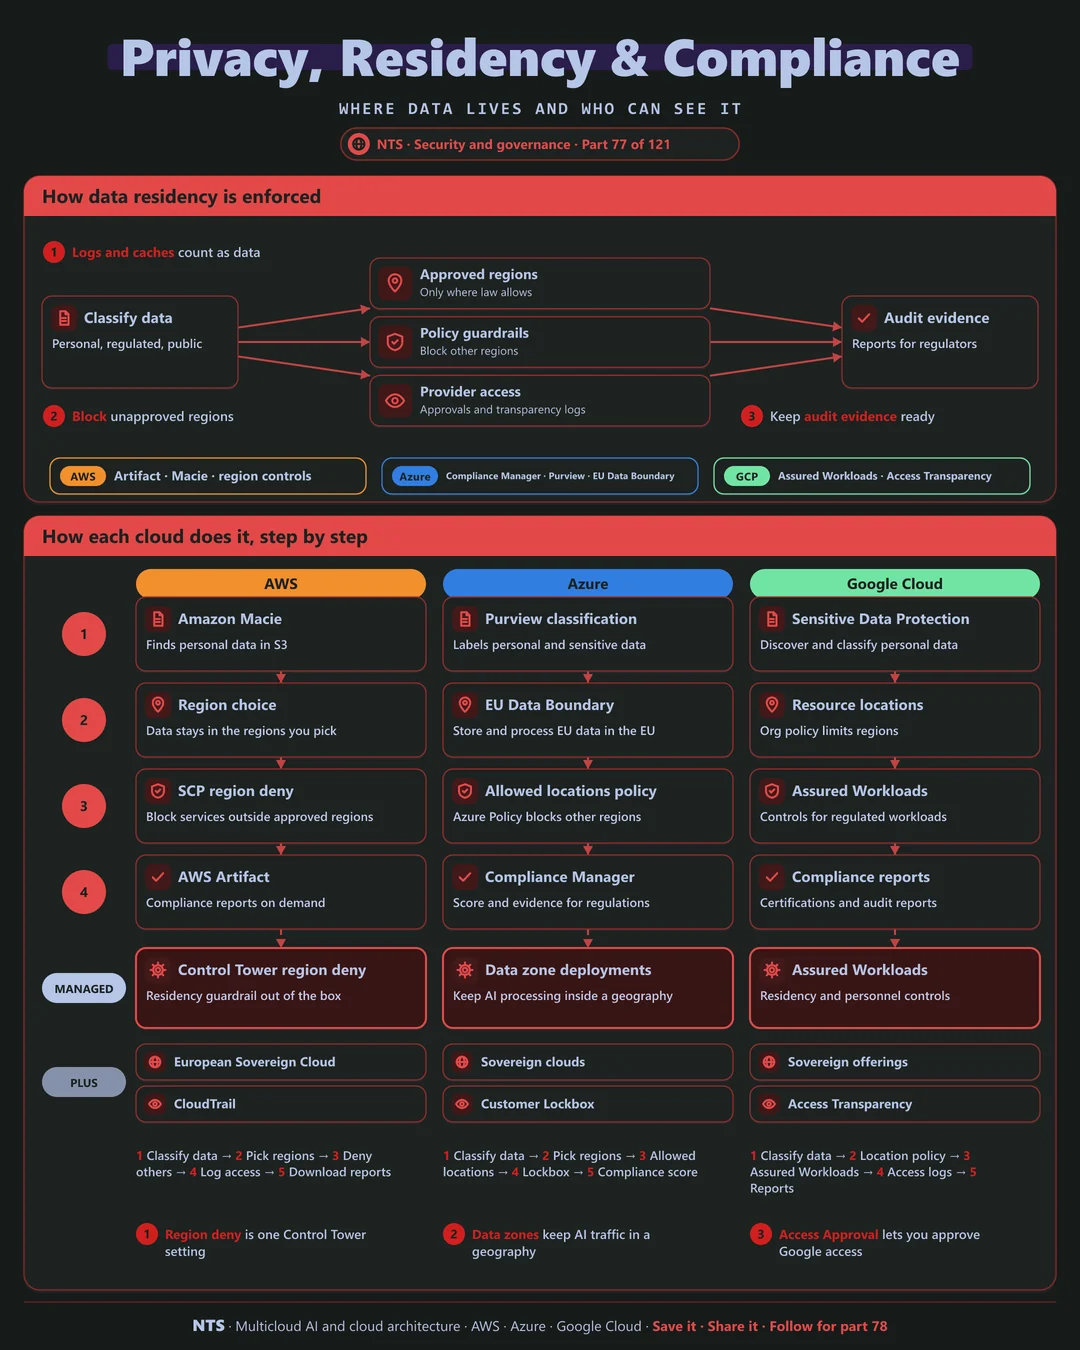
Classify data first, then pick approved regions. Policy guardrails block resources and AI deployments elsewhere. Control and log provider access, and keep audit evidence ready from the provider's compliance reports and your own logs.
AWS, Azure and Google Cloud compared
| AWS | Azure | Google Cloud | |
|---|---|---|---|
| Region restriction | SCP region deny, Control Tower | Allowed locations policy | Resource locations org policy |
| AI processing boundary | Region-specific inference | Data zone deployments, EU Data Boundary | Regional endpoints, data residency |
| Sensitive data discovery | Amazon Macie | Microsoft Purview | Sensitive Data Protection |
| Provider access control | Nitro System design | Customer Lockbox | Access Approval, Access Transparency |
| Compliance evidence | AWS Artifact | Compliance Manager, Service Trust Portal | Compliance reports manager |
What makes each cloud different
AWS
AWS keeps data in the regions you choose, Control Tower offers a region deny control in one setting and AWS Artifact provides audit reports on demand. The European Sovereign Cloud adds EU-only operations.
Azure
Azure's EU Data Boundary keeps EU customer data in the EU, data zone deployments keep AI processing within a geography and Customer Lockbox requires your approval for Microsoft engineer access.
Google Cloud
Google Cloud's resource location constraint limits regions, Assured Workloads adds controls for regulated workloads and Access Transparency logs every action Google staff take on your data.
Design decisions that matter
- 01Map every AI data flow
Prompts, outputs, logs, caches, indexes.
- 02Deny unapproved regions
At the organization level.
- 03Approve provider access
Where the regulation requires it.
- 04Keep evidence current
Reports and logs ready for auditors.
Common mistakes we see
- Global AI endpoints for regulated data. Processing may leave the region.
- Logs stored elsewhere. Prompts end up in another country.
- Residency checked once. New services slip through later.
A practical 30-day plan
- Week 1
Classify data and list legal requirements.
- Week 2
Map AI data flows and storage locations.
- Week 3
Apply region policies and AI processing boundaries.
- Week 4
Assemble audit evidence and review provider access.
How NTS helps
NTS designs privacy and residency controls for cloud and AI on AWS, Azure and Google Cloud, covering data mapping, region guardrails, provider access controls and audit readiness for GDPR and sector rules.
What you get
- A data residency map across clouds and regions
- Privacy controls for personal data
- Compliance mapping for GDPR, HIPAA and more
- Evidence collection for audits
Typical outcomes
- Faster, smoother audits
- Personal data handled correctly
- Confidence entering regulated markets
How we work with you
- 1Assess
A focused review of your privacy, residency and compliance across AWS, Azure and Google Cloud. We look for the gaps we find most often: global AI endpoints for regulated data, logs stored elsewhere and residency checked once.
- 2Design
A target architecture and roadmap built on the decisions that matter most: map every AI data flow, deny unapproved regions, approve provider access and keep evidence current.
- 3Build
Hands-on delivery alongside your team. We classify data and list legal requirements, map AI data flows and storage locations, apply region policies and AI processing boundaries, and finally assemble audit evidence and review provider access.
- 4Run and improve
We track regulatory changes and update controls and evidence accordingly.
Why teams choose NTS for privacy, residency and compliance
- Compliance made practical
We turn regulations into concrete technical controls.
- Residency by design
Data stays where the law says it must.
- Audit-ready evidence
Automated evidence saves weeks of audit preparation.
Book a free 30-minute review
Talk to an NTS architect about your privacy, residency and compliance on AWS, Azure and Google Cloud.