
Multicloud AI & ERP / Cloud & AI Security, Governance & Compliance
Why it matters
Certificates secure every HTTPS connection and many internal services. Shorter certificate lifetimes across the industry make manual renewal impossible to sustain, and a single missed expiry can take down customer-facing services.
How it works
An automated lifecycle
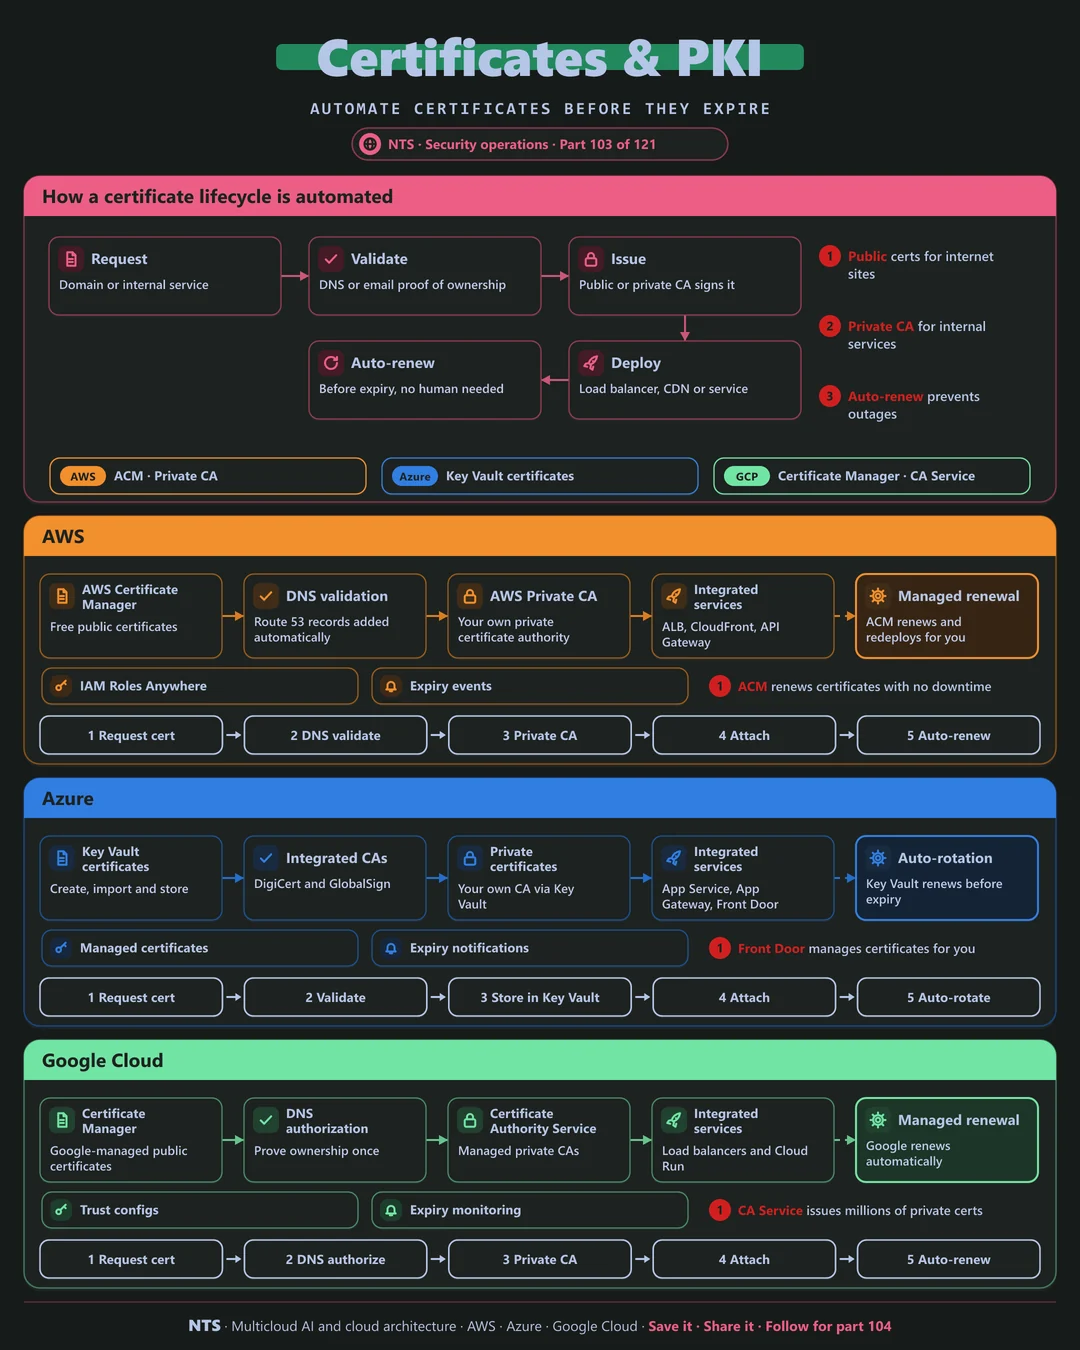
A service requests a certificate, ownership is validated through DNS, a public or private CA issues it, it is deployed to load balancers and services, and it is renewed automatically before expiry with no human involved.
AWS, Azure and Google Cloud compared
| AWS | Azure | Google Cloud | |
|---|---|---|---|
| Public certificates | AWS Certificate Manager | App Service managed certificates, Key Vault | Certificate Manager |
| Private CA | AWS Private CA | Key Vault with private CA integration | Certificate Authority Service |
| Auto-renewal | Managed renewal | Key Vault auto-rotation | Managed renewal |
| Integrated services | ALB, CloudFront, API Gateway | App Service, App Gateway, Front Door | Load balancers, Cloud Run |
| Certificates as identity | IAM Roles Anywhere | Managed identity alternatives | Workload certificates, mTLS |
What makes each cloud different
AWS
AWS Certificate Manager issues free public certificates and renews them with no downtime when attached to integrated services, and AWS Private CA runs your own private certificate authority.
Azure
Azure Key Vault stores and rotates certificates from integrated CAs, and services such as Front Door and App Service can manage certificates entirely for you.
Google Cloud
Google's Certificate Manager provides managed public certificates with DNS authorization, and Certificate Authority Service issues private certificates at very high scale.
Design decisions that matter
- 01Managed certificates everywhere possible
No manual renewals.
- 02A private CA for internal services
Not self-signed certificates.
- 03Inventory every certificate
Including ones outside the cloud.
- 04Alert well before expiry
For anything not auto-renewed.
Common mistakes we see
- Spreadsheet tracking. Someone always misses one.
- Self-signed internal certs. Trust warnings and no revocation.
- Long-lived certificates. Industry lifetimes are shrinking.
A practical 30-day plan
- Week 1
Inventory all certificates and expiry dates.
- Week 2
Move public endpoints to managed certificates.
- Week 3
Set up a private CA for internal services.
- Week 4
Add expiry monitoring for the rest.
How NTS helps
NTS automates certificate management on AWS, Azure and Google Cloud, covering inventory, managed public certificates, private CAs and monitoring, so expiry never causes an outage again.
What you get
- A full inventory of certificates and expiry dates
- Managed certificates with automatic renewal
- A private CA design for internal services
- Expiry monitoring and alerting
Typical outcomes
- Zero certificate-related outages
- No spreadsheet tracking
- Internal services secured with trusted certificates
How we work with you
- 1Assess
A focused review of your certificate and PKI management across AWS, Azure and Google Cloud. We look for the gaps we find most often: spreadsheet tracking, self-signed internal certs and long-lived certificates.
- 2Design
A target architecture and roadmap built on the decisions that matter most: managed certificates everywhere possible, a private CA for internal services, inventory every certificate and alert well before expiry.
- 3Build
Hands-on delivery alongside your team. We inventory all certificates and expiry dates, move public endpoints to managed certificates, set up a private CA for internal services, and finally add expiry monitoring for the rest.
- 4Run and improve
We monitor certificate health, onboard new services and keep PKI policies current.
Why teams choose NTS for certificate and PKI management
- No more expiry outages
Automation removes the human error behind most certificate incidents.
- PKI done properly
We design private CAs that scale securely.
- Ready for shorter lifetimes
Automation prepares you for shrinking certificate validity periods.
Book a free 30-minute review
Talk to an NTS architect about your certificate and PKI management on AWS, Azure and Google Cloud.