
Multicloud AI & ERP / Cloud & AI Security, Governance & Compliance
Why it matters
Personal, financial and health data spreads across storage, databases and SaaS. Generative AI adds a new exit: employees pasting sensitive data into prompts. DLP finds that data and stops it leaking.
How it works
Discover, classify, control
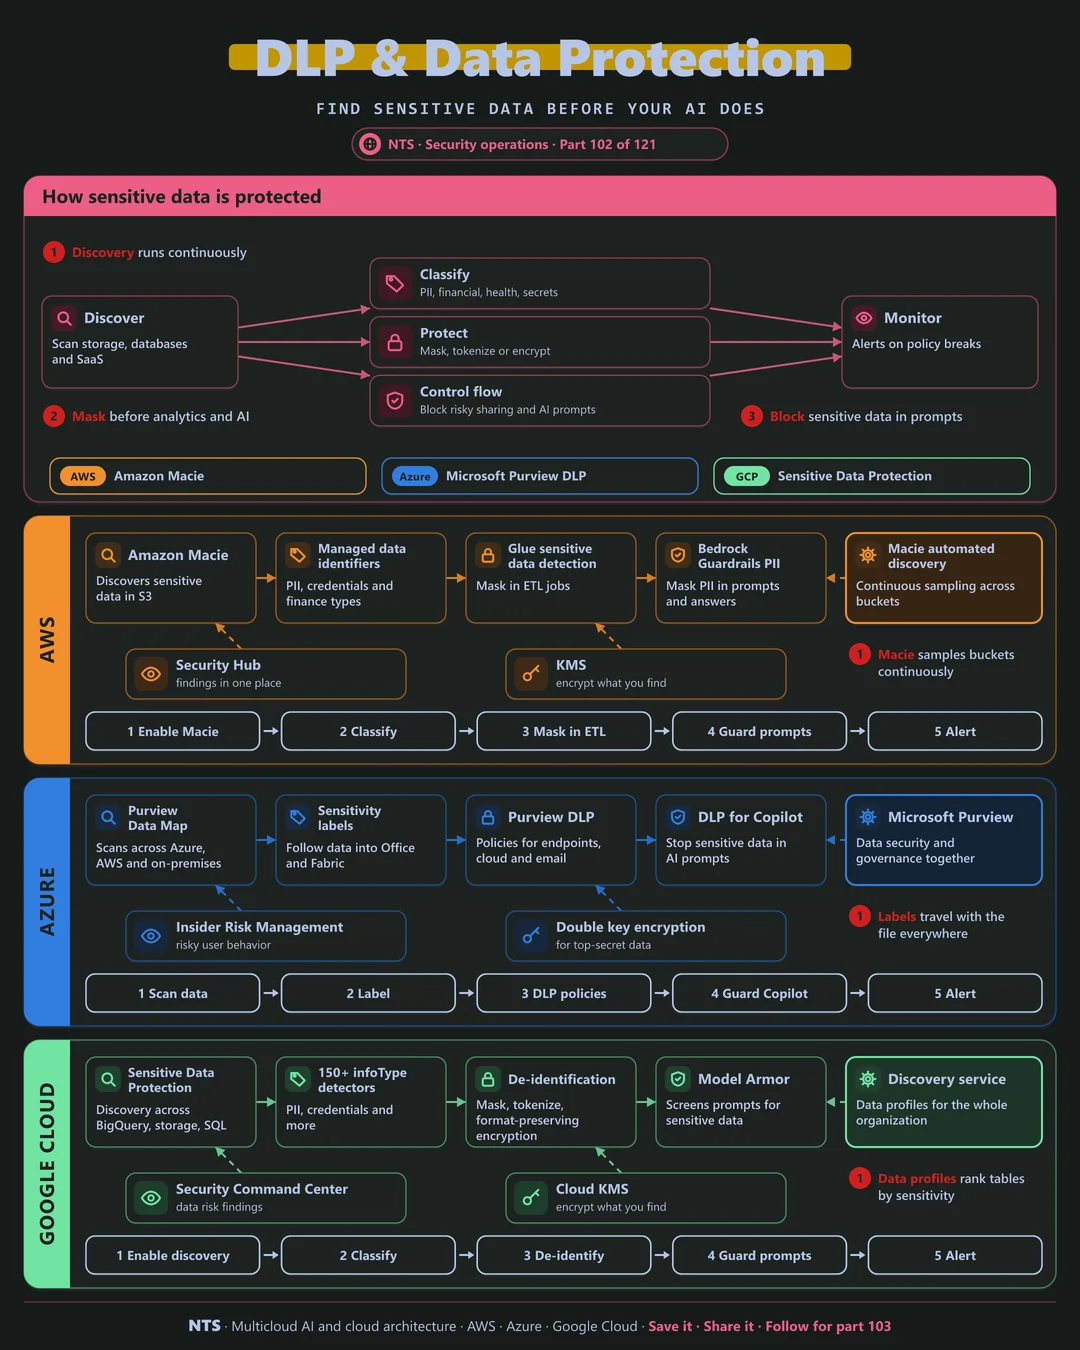
Discover sensitive data across storage, databases and SaaS. Classify it as personal, financial, health or secret. Protect it with masking, tokenization or encryption, control where it flows, including AI prompts, and monitor for policy breaks.
AWS, Azure and Google Cloud compared
| AWS | Azure | Google Cloud | |
|---|---|---|---|
| Discovery | Amazon Macie | Microsoft Purview Data Map | Sensitive Data Protection discovery |
| Labels | Tags and Macie findings | Sensitivity labels | Data profiles and tags |
| Masking and tokenization | Glue sensitive data detection | Dynamic data masking, Purview | De-identification, format-preserving encryption |
| AI prompt protection | Bedrock Guardrails PII filters | Purview DLP for Copilot | Model Armor |
| Insider risk | GuardDuty findings | Insider Risk Management | Security Command Center |
What makes each cloud different
AWS
Amazon Macie continuously samples S3 to find sensitive data, Glue masks it in ETL jobs and Bedrock Guardrails mask personal data in prompts and answers.
Azure
Microsoft Purview scans across Azure, other clouds and on-premises, applies sensitivity labels that travel with files into Office and Fabric, and extends DLP to Microsoft 365 Copilot prompts.
Google Cloud
Google's Sensitive Data Protection profiles data across the organization with more than 150 detectors and de-identifies it with masking, tokenization and format-preserving encryption.
Design decisions that matter
- 01Discover continuously
New data arrives every day.
- 02Label at creation where possible
Protection follows the data.
- 03Mask before analytics and AI
Use the minimum identifiable data.
- 04DLP for AI prompts
The newest leak path.
Common mistakes we see
- One-off discovery projects. Results go stale within months.
- Blocking everything. Users route around controls.
- Forgetting AI tools. Sensitive data pasted into public chatbots.
A practical 30-day plan
- Week 1
Turn on automated discovery.
- Week 2
Agree classification labels and owners.
- Week 3
Apply masking and DLP policies.
- Week 4
Extend controls to AI tools and prompts.
How NTS helps
NTS implements data protection with Macie, Purview and Sensitive Data Protection, covering discovery, labeling, masking and DLP policies that extend to generative AI.
What you get
- Discovery of sensitive data across clouds
- Classification and labeling
- DLP policies for email, storage and AI tools
- Monitoring and incident handling
Typical outcomes
- Sensitive data found and protected
- Fewer data leaks
- Compliance with privacy regulations
How we work with you
- 1Assess
A focused review of your data loss prevention across AWS, Azure and Google Cloud. We look for the gaps we find most often: one-off discovery projects, blocking everything and forgetting AI tools.
- 2Design
A target architecture and roadmap built on the decisions that matter most: discover continuously, label at creation where possible, mask before analytics and AI and DLP for AI prompts.
- 3Build
Hands-on delivery alongside your team. We turn on automated discovery, agree classification labels and owners, apply masking and DLP policies, and finally extend controls to AI tools and prompts.
- 4Run and improve
We tune policies, investigate incidents and extend coverage to new data sources.
Why teams choose NTS for data loss prevention
- Know your data first
We find sensitive data before protecting it.
- Protection without disruption
Policies are tuned so work continues smoothly.
- Covers AI tools too
We stop sensitive data leaking into AI prompts.
Book a free 30-minute review
Talk to an NTS architect about your data loss prevention on AWS, Azure and Google Cloud.