
Multicloud AI & ERP / Agentic AI & Cloud AI Infrastructure
Why it matters
As agents multiply, so do risks: agents acting with a human's full permissions, memories holding sensitive data indefinitely, and nobody knowing which agents exist. Governance must scale with adoption.
How it works
The controls
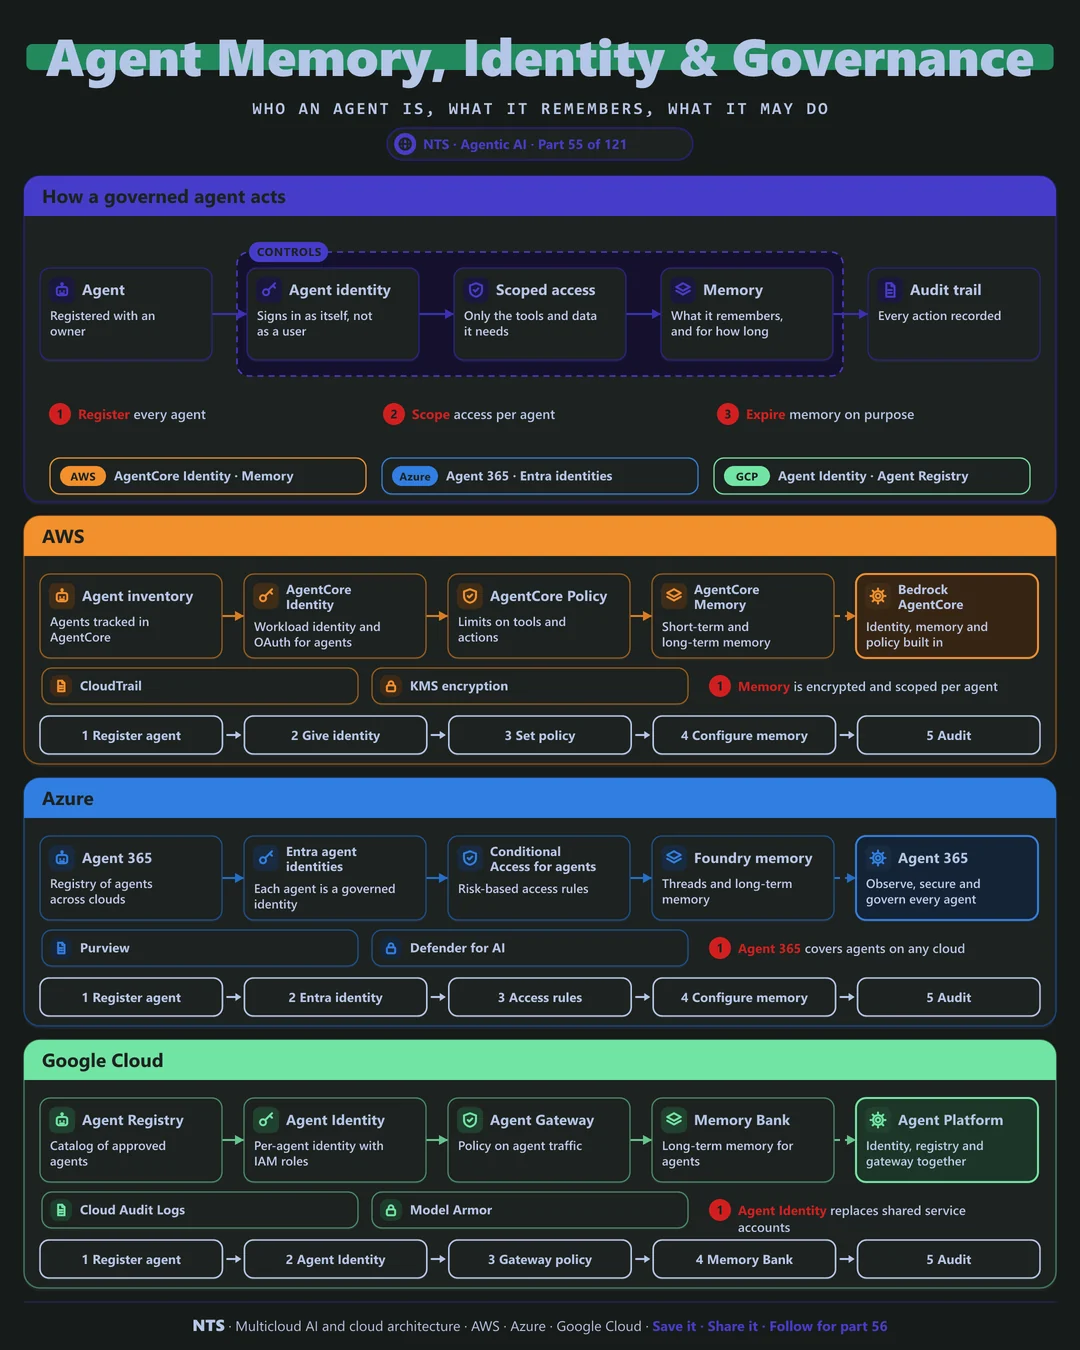
Every agent is registered with an owner. It signs in with its own agent identity, never a person's credentials. Scoped access limits it to the tools and data it needs. Memory has clear retention rules, and an audit trail records every action.
AWS, Azure and Google Cloud compared
| AWS | Azure | Google Cloud | |
|---|---|---|---|
| Agent registry | AgentCore inventory | Agent 365 | Agent Registry |
| Agent identity | AgentCore Identity | Entra agent identities | Agent Identity |
| Access policy | AgentCore Policy | Conditional Access for agents | Agent Gateway policy |
| Memory | AgentCore Memory | Foundry memory | Memory Bank |
| Audit | CloudTrail | Entra and Purview logs | Cloud Audit Logs |
What makes each cloud different
AWS
AgentCore combines identity, memory and policy: agents get workload identities and OAuth to tools, memory is encrypted and scoped, and CloudTrail records agent API calls.
Azure
Agent 365 gives organizations a registry, identity and governance layer for agents across clouds, built on Entra so each agent is a governed identity with Conditional Access and Purview data protection.
Google Cloud
Agent Identity replaces shared service accounts with per-agent identities, Agent Registry catalogs approved agents and Agent Gateway enforces policy on agent traffic.
Design decisions that matter
- 01Register every agent
Owner, purpose and data access on record.
- 02Agent identities, not user credentials
Scoped, reviewable and revocable.
- 03Retention rules for memory
Expire what is not needed.
- 04Audit like privileged users
Log and review agent actions.
Common mistakes we see
- Agents using a person's account. Every action looks like that person.
- Unlimited memory. Sensitive data stays forever.
- Shadow agents. Teams deploy agents nobody knows about.
A practical 30-day plan
- Week 1
Inventory existing agents and owners.
- Week 2
Move agents to their own identities.
- Week 3
Scope access and set memory retention.
- Week 4
Turn on auditing and a review cadence.
How NTS helps
NTS builds agent governance on AWS, Azure and Google Cloud: registries, agent identities, access policies, memory controls and auditing, so AI agents scale safely across the enterprise.
What you get
- Agent identities with least-privilege access
- Memory design with retention and privacy rules
- An agent registry with owners and approvals
- Audit logging and kill switches
Typical outcomes
- Every agent known, owned and auditable
- Reduced risk from agent mistakes
- Compliance-ready agent operations
How we work with you
- 1Assess
A focused review of your agent memory, identity and governance across AWS, Azure and Google Cloud. We look for the gaps we find most often: agents using a person's account, unlimited memory and shadow agents.
- 2Design
A target architecture and roadmap built on the decisions that matter most: register every agent, agent identities, not user credentials, retention rules for memory and audit like privileged users.
- 3Build
Hands-on delivery alongside your team. We inventory existing agents and owners, move agents to their own identities, scope access and set memory retention, and finally turn on auditing and a review cadence.
- 4Run and improve
We review agent permissions, memory and logs regularly, and onboard new agents through the registry.
Why teams choose NTS for agent memory, identity and governance
- Governance before scale
We put controls in place before agents multiply.
- Identity expertise
We treat agents as first-class identities with proper access.
- Privacy-aware memory
Agents remember what helps and forget what they should.
Book a free 30-minute review
Talk to an NTS architect about your agent memory, identity and governance on AWS, Azure and Google Cloud.